16 min
10 AWS DevOps Practices We Actually Use in Production in 2026
Real AWS DevOps practices from production: GitOps on EKS, OpenTelemetry, supply chain security, chaos engineering with FIS, and AI-assisted DevOps with Amazon Q.
 Manoj V.
Blog category
Real AWS DevOps practices from production: GitOps on EKS, OpenTelemetry, supply chain security, chaos engineering with FIS, and AI-assisted DevOps with Amazon Q.
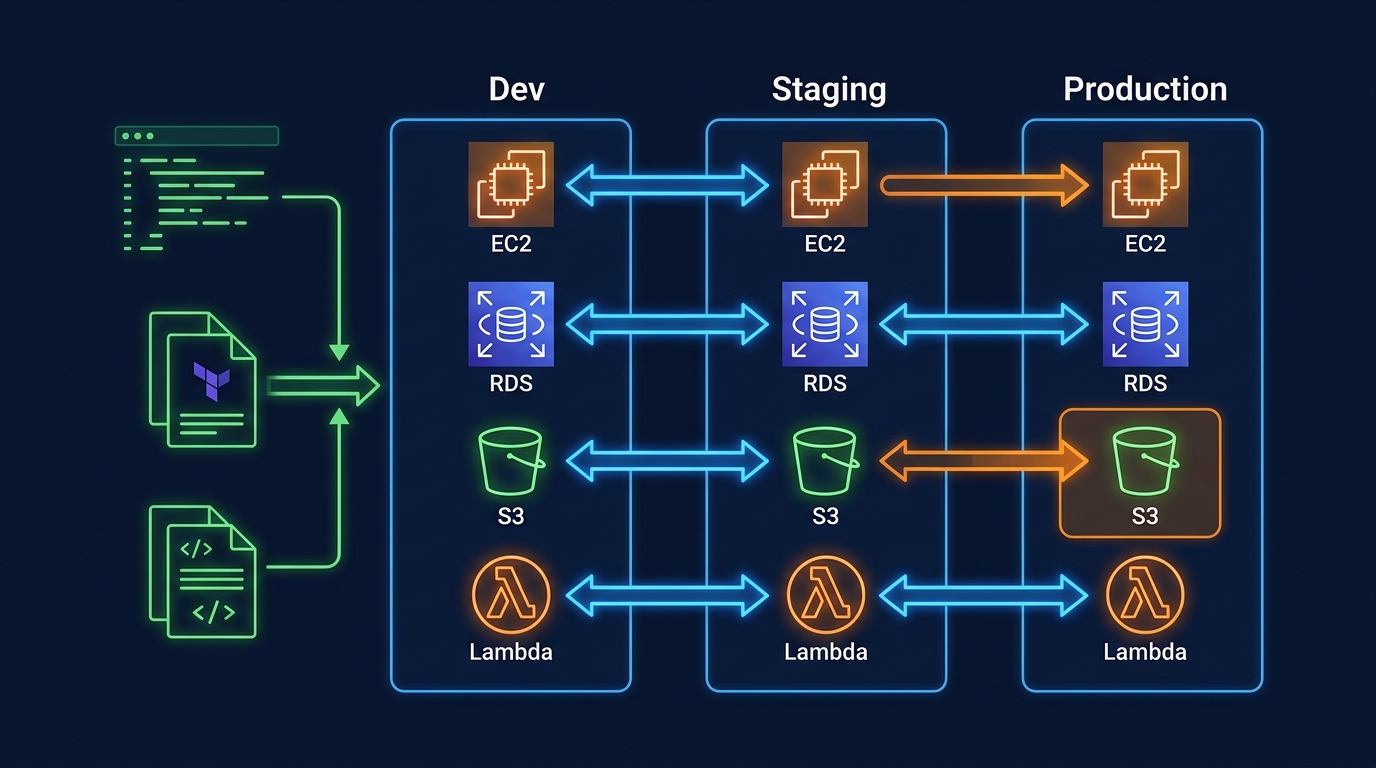
Manoj V.When staging is green and prod fails, it's usually config drift, not the commit. July 2026 refresh: IaC parity, intentional size deltas, drift checks that catch SG and parameter-group surprises.
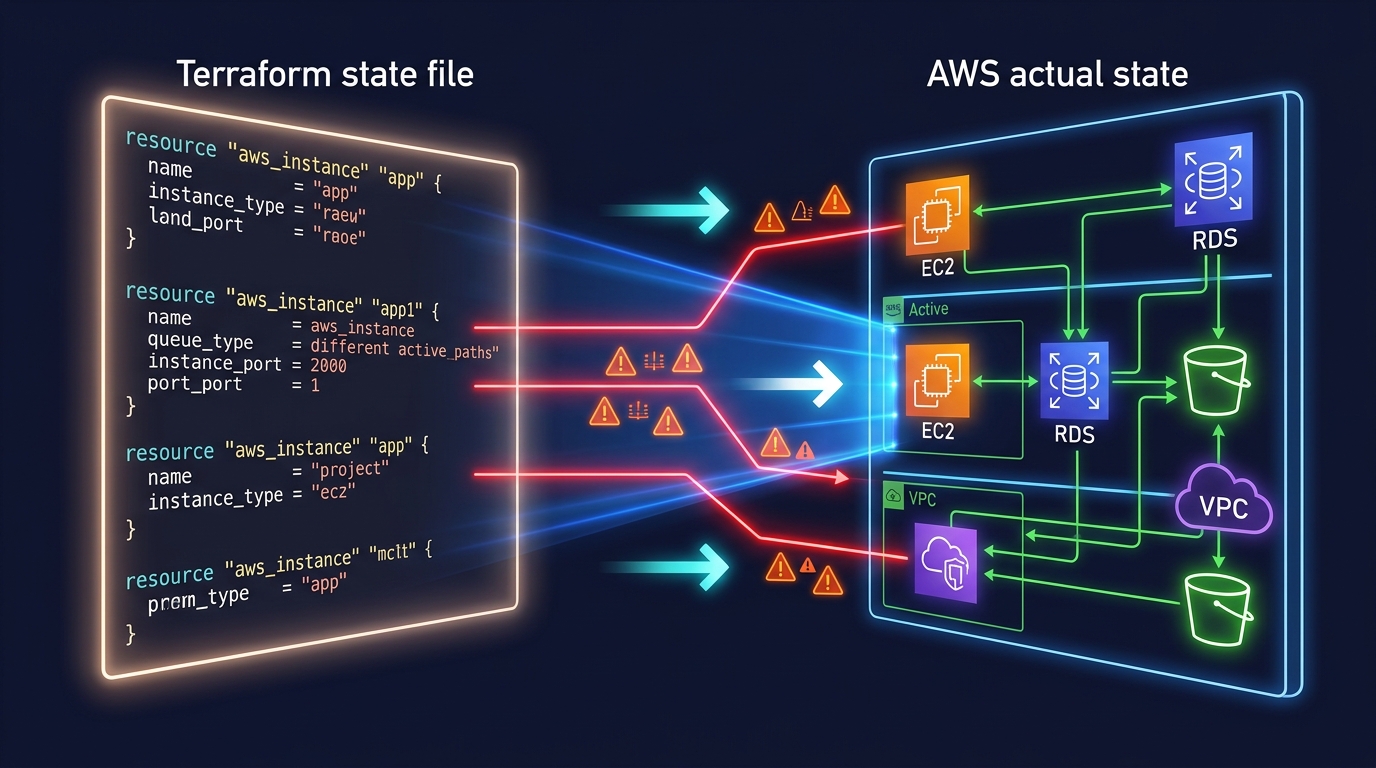
Manoj V.Detect AWS config drift with terraform plan + Config. July 2026 runbook: schedule, triage, prevent console writes.
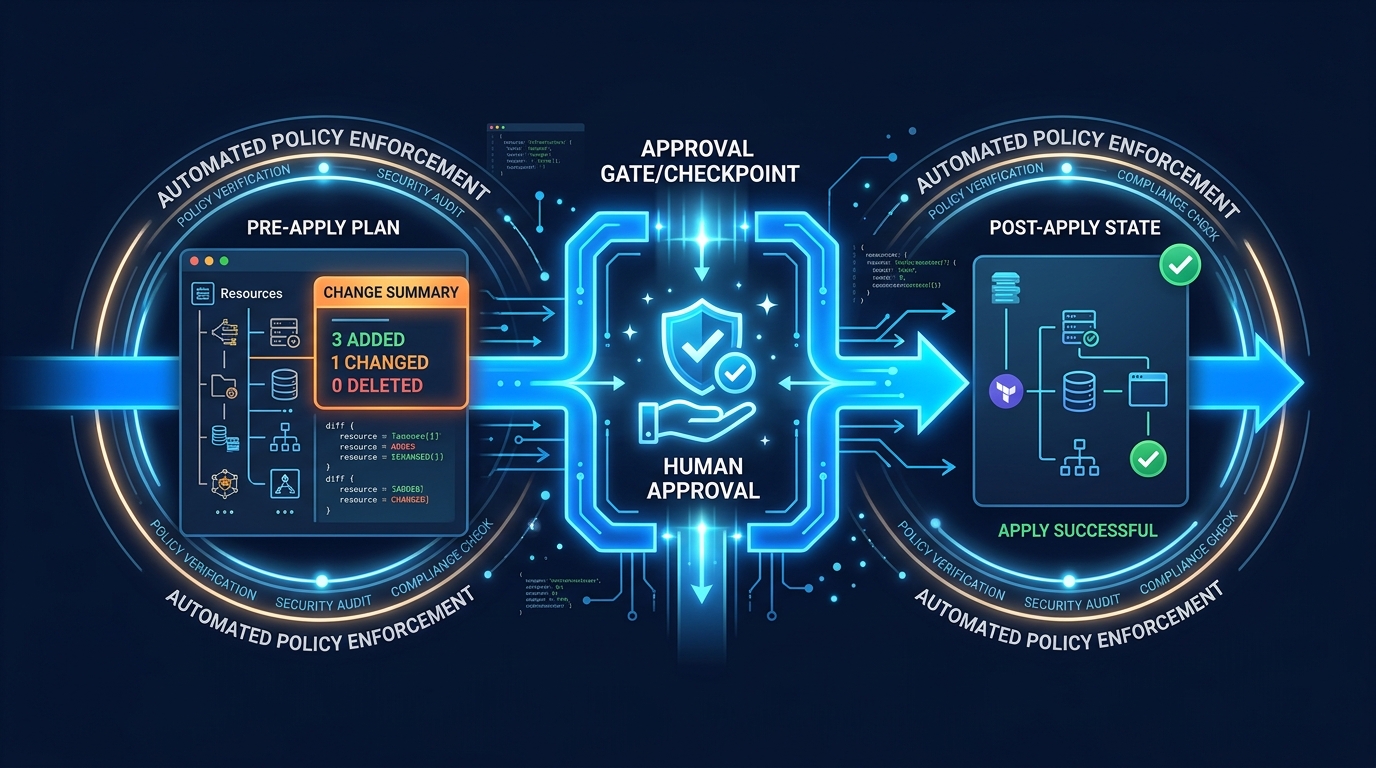
Manoj V.One bad `terraform apply` still deletes databases. July 2026: plan, review, apply, no -auto-approve, OIDC CI, Atlantis/HCP Terraform gates.
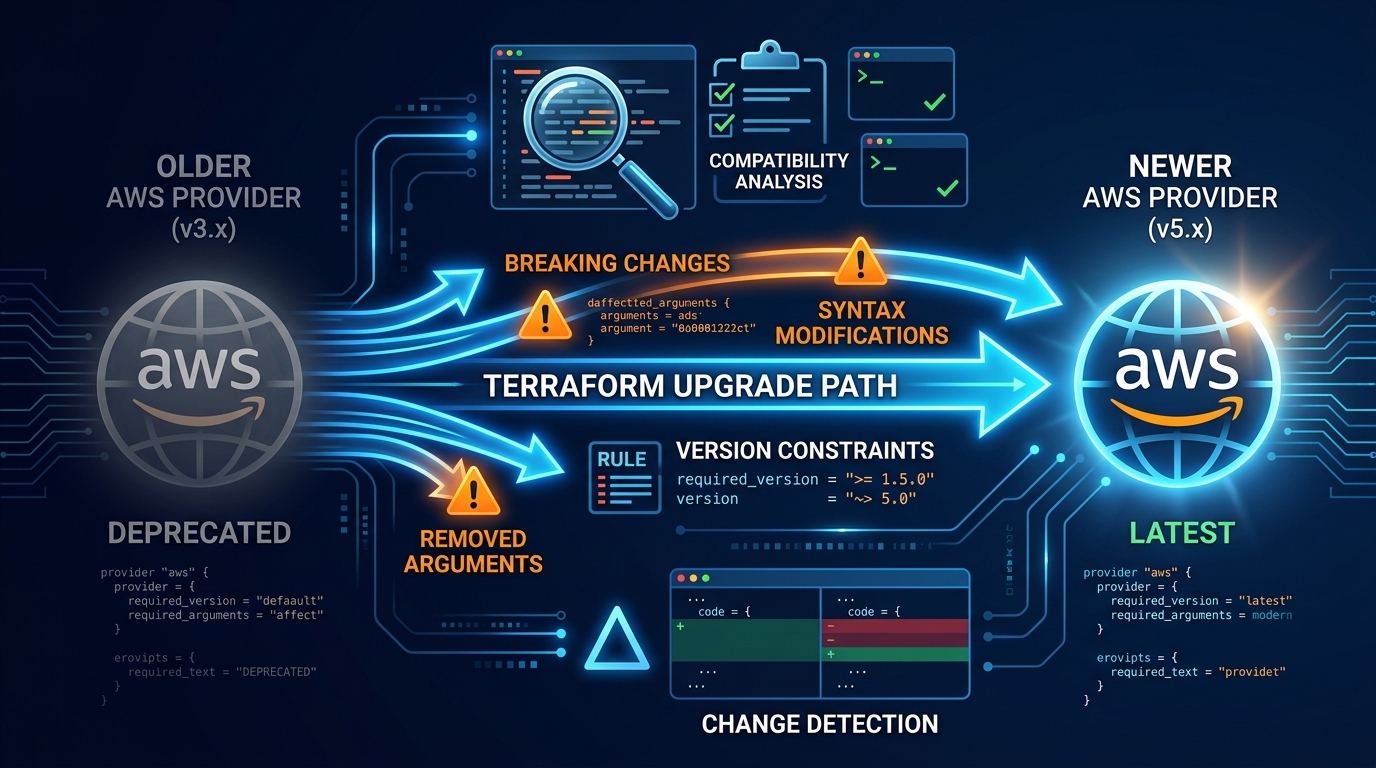
Manoj V.AWS provider 6.0 GA June 2025. July 2026: upgrade 4 to 5 to 6 one major at a time, changelog-first, staging plan, lockfile commit.
Manoj V.Terraform on AWS: import, state mv/rm, stuck locks. July 2026: S3 use_lockfile (TF 1.10+); DynamoDB locking is legacy.
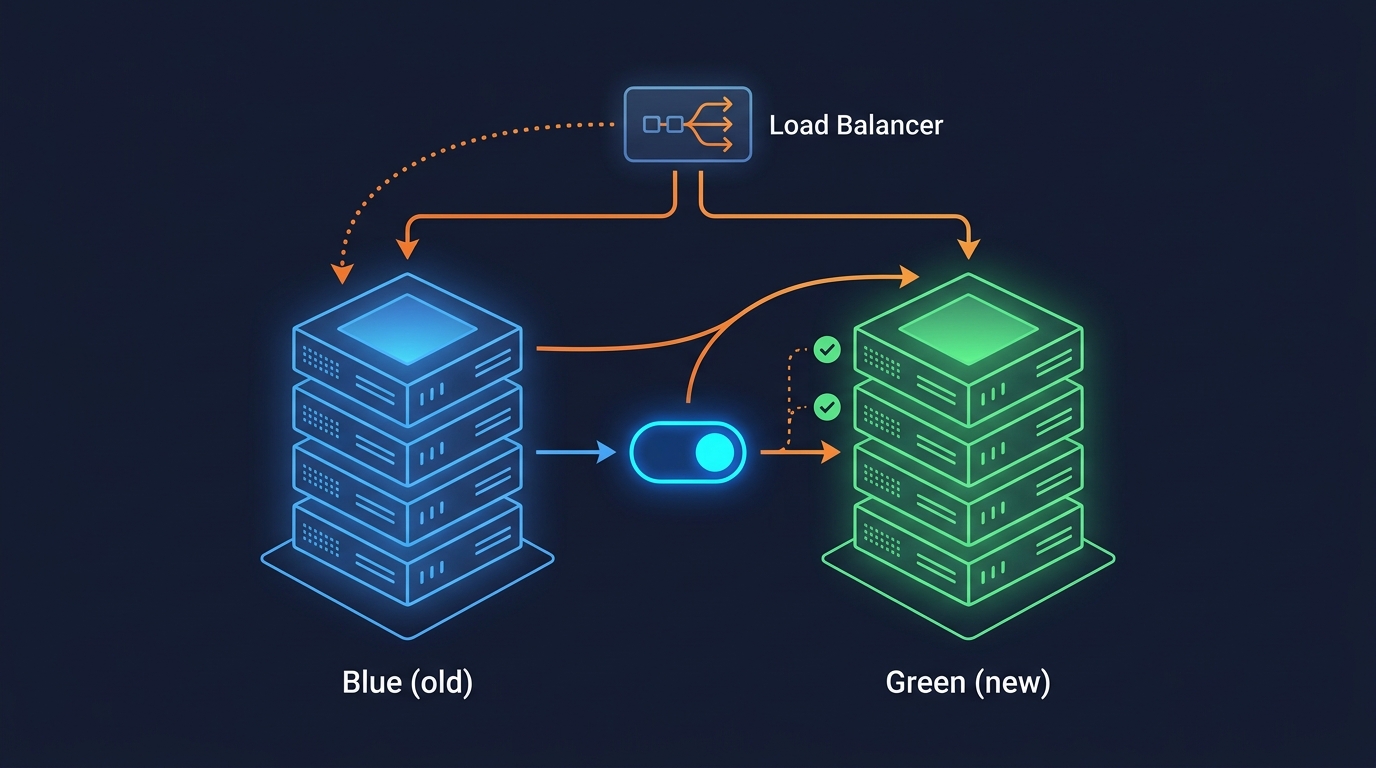
Manoj V.ECS blue/green without downtime: CodeDeploy canary/linear still works, and native ECS BLUE_GREEN (2025+) is now a first-class path. July 2026 checklist: hooks, alarms, dual-run cost.
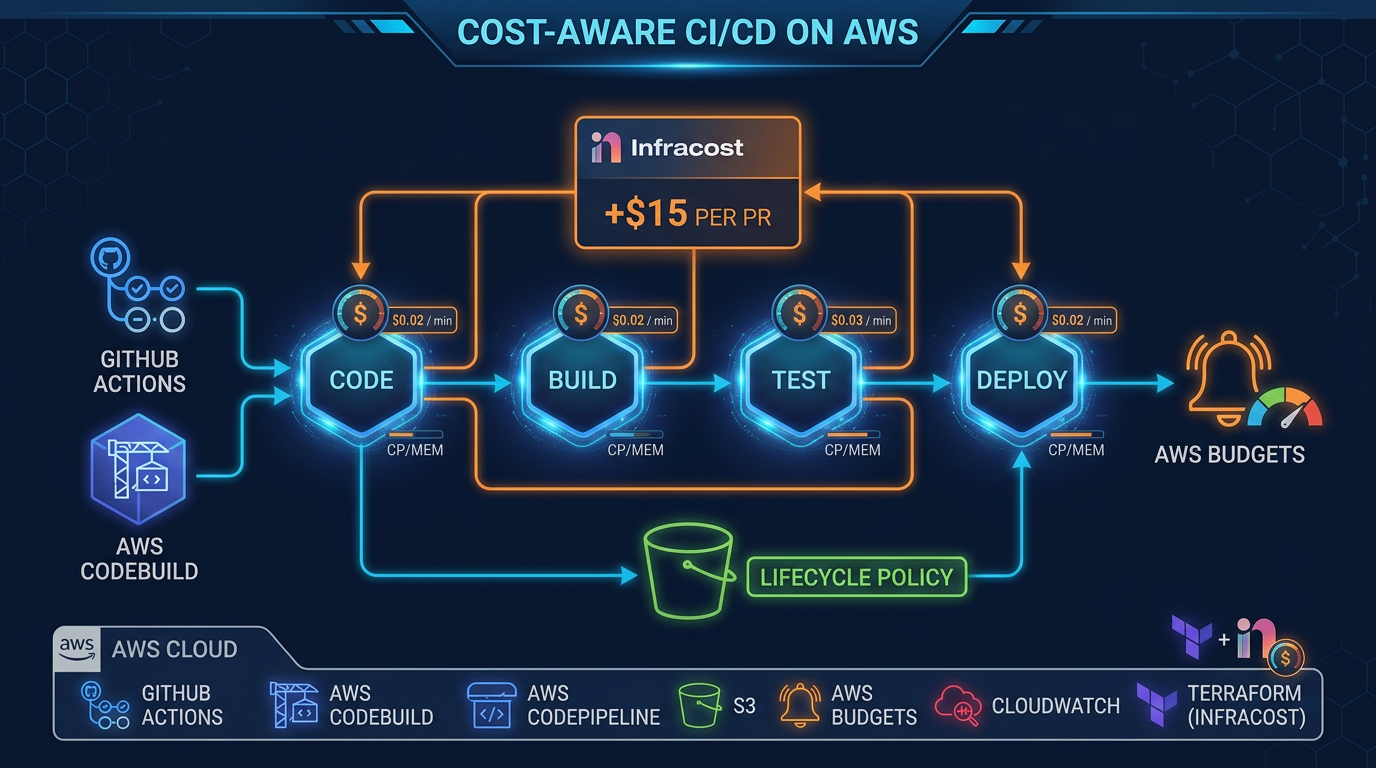
Manoj V.CI/CD infrastructure is invisible until your DevOps bill hits $15,000/month. Build minutes, artifact storage, and ephemeral environments accumulate costs that few teams track. This post covers how to measure and control them.
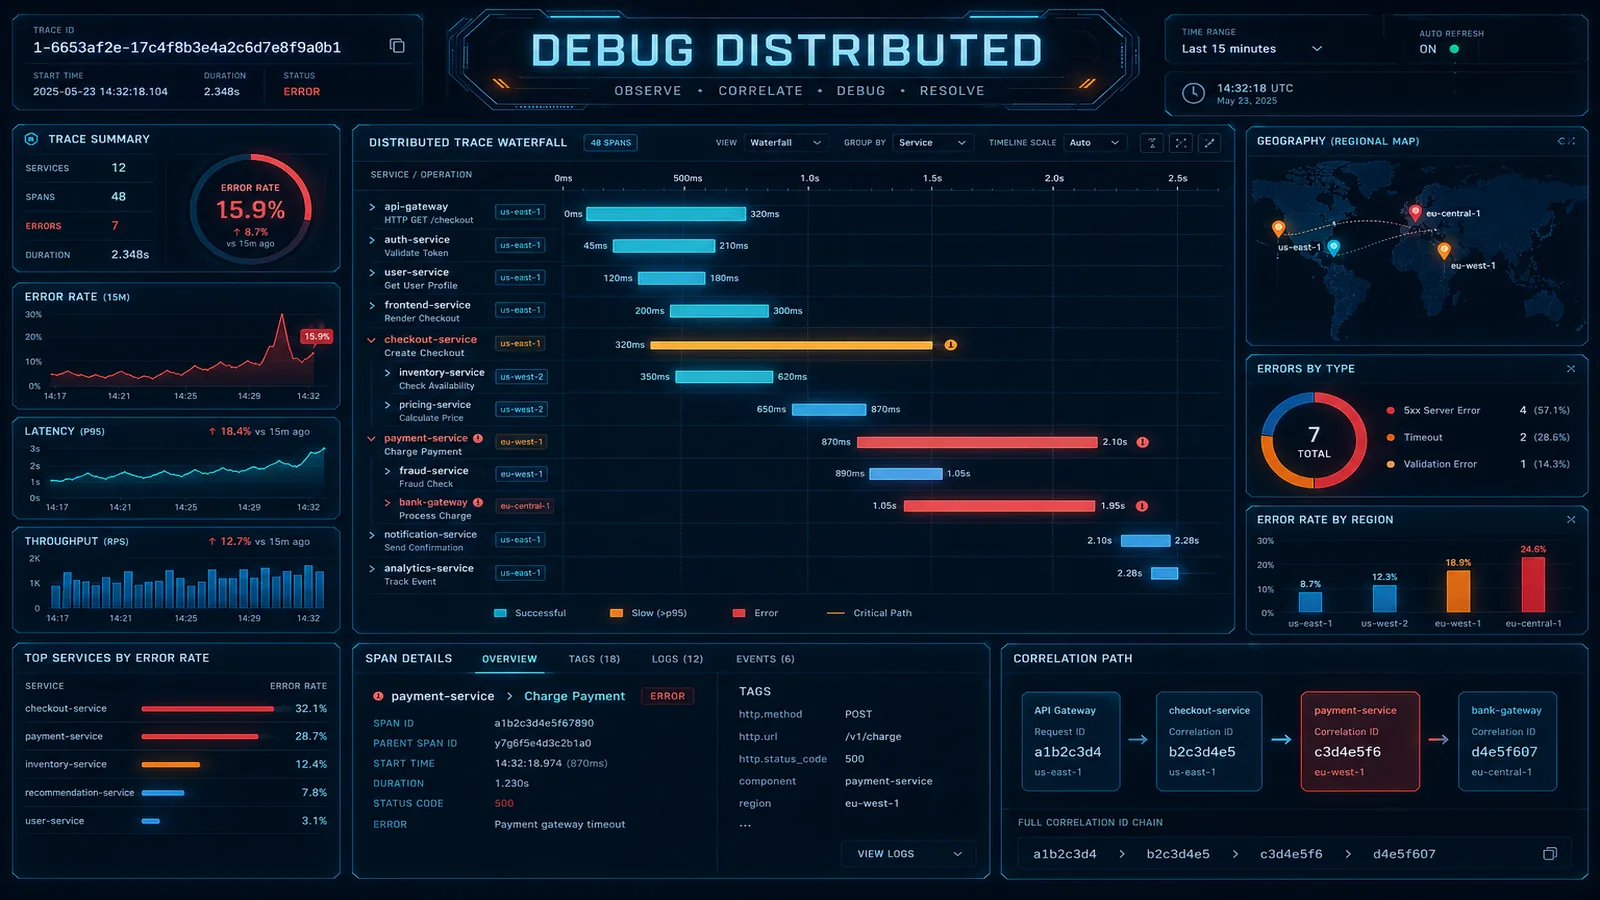
Manoj V.A 500ms latency spike in a distributed system could be a slow RDS query, a Lambda cold start, a downstream API timeout, or a CloudWatch Logs ingestion delay. Finding the cause requires correlated logs, traces, and metrics, not grep.
Manoj V.Vite 8 (March 2026) ships Rolldown by default. July 2026: Bun install, SWC, CodeBuild cache to cut CI build minutes.
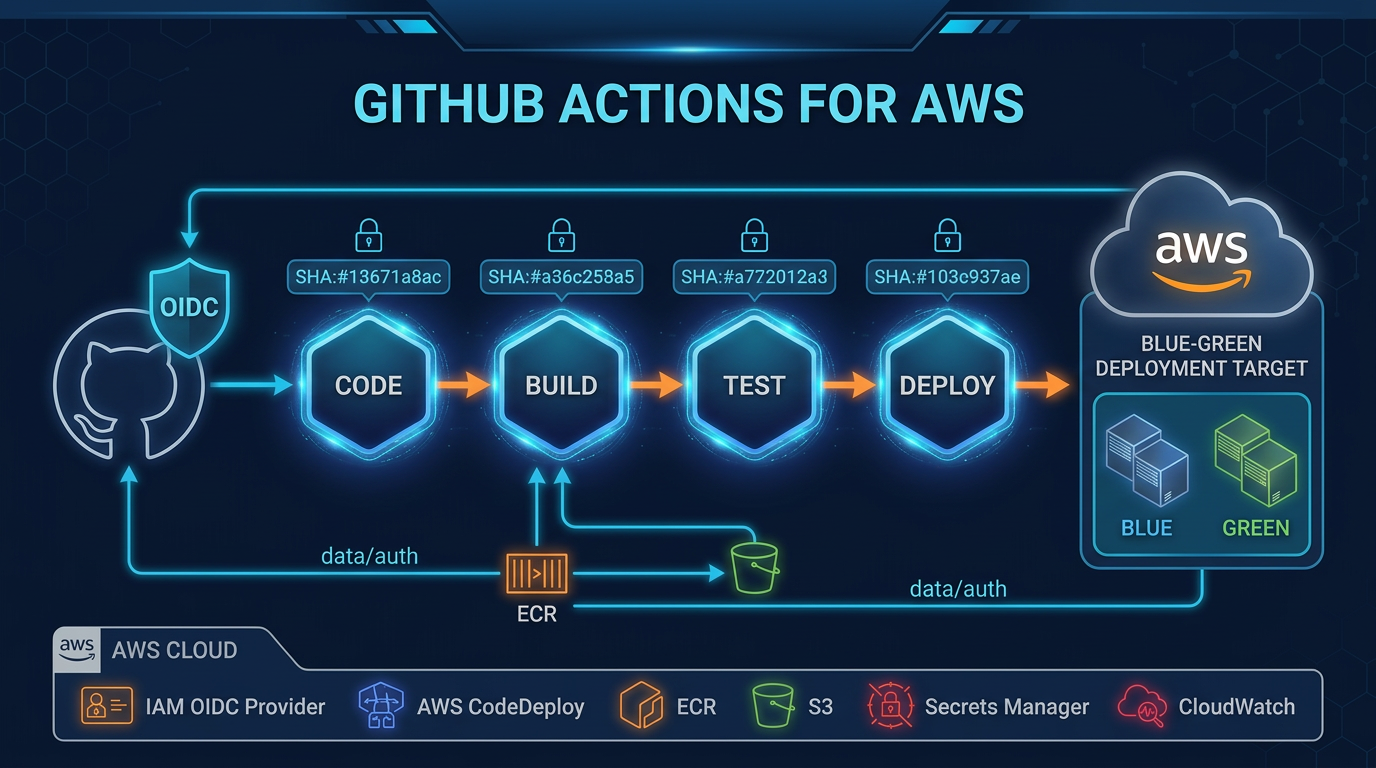
Manoj V.GitHub Actions patterns for AWS workloads in production: OIDC authentication, pinned actions, blue-green deployments, build caching, and the security mistakes that leave your pipeline open to supply chain attacks.
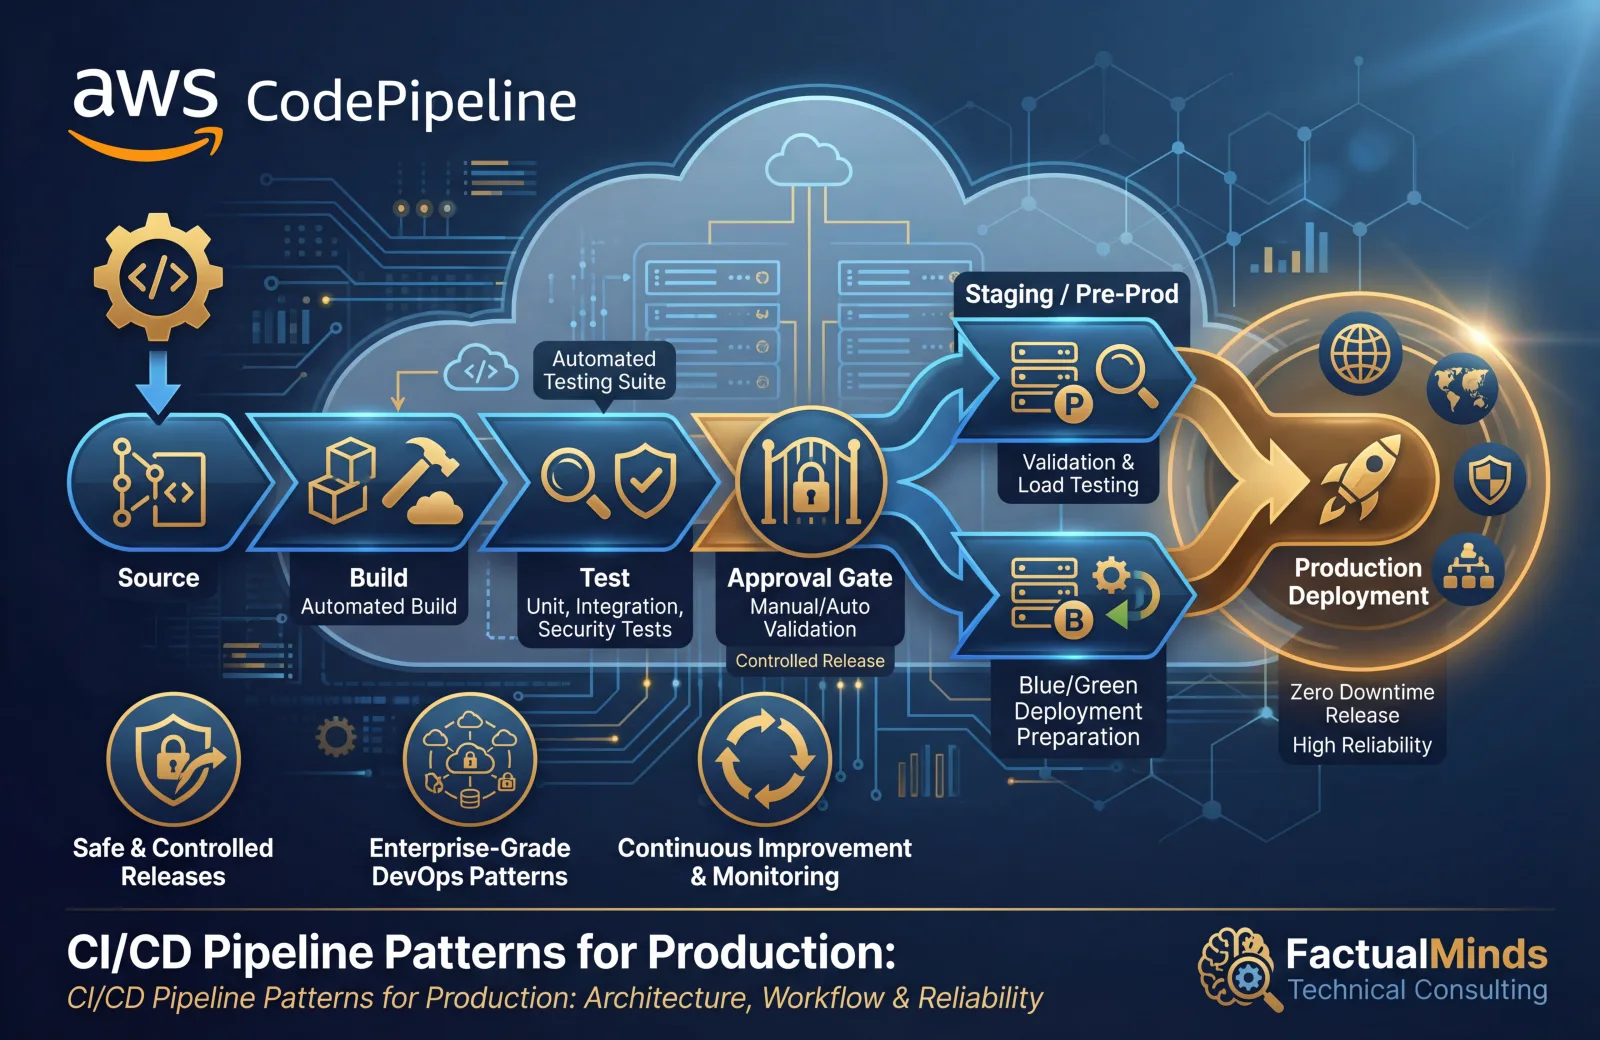
Manoj V.CodePipeline isn't the most loved CI/CD tool, but it talks to every other AWS service natively. Pipeline architecture, CodeBuild configuration, cross-account deploys, and the patterns that ship code safely without bolting on a third-party runner.
Manoj V.