Terraform vs CloudFormation on AWS (2026): Enterprise IaC Decision Guide
Quick summary: On a 40-account AWS Organization, platform baseline via CloudFormation StackSets (Hooks, GuardDuty enroll) plus app teams on Terraform/OpenTofu cut org-wide guardrail rollout from 9 weeks to 3 — without forcing one tool for everything.
Key Takeaways
- CloudFormation Hooks deploy org-wide via service-managed StackSets — AWS documents the pattern for baseline guardrails across OUs without per-account CLI runs
- Terraform 1
- 8+ and OpenTofu 1
- 8+ remain the default for application teams with existing modules and multi-provider needs
- This post is Terraform/OpenTofu vs CloudFormation/StackSets for enterprise AWS
Table of Contents
CloudFormation Hooks deploy org-wide via service-managed StackSets — AWS documents the pattern for baseline guardrails across OUs without per-account CLI runs. Terraform 1.8+ and OpenTofu 1.8+ remain the default for application teams with existing modules and multi-provider needs. The enterprise question is not “which one wins” but which layer each tool owns.
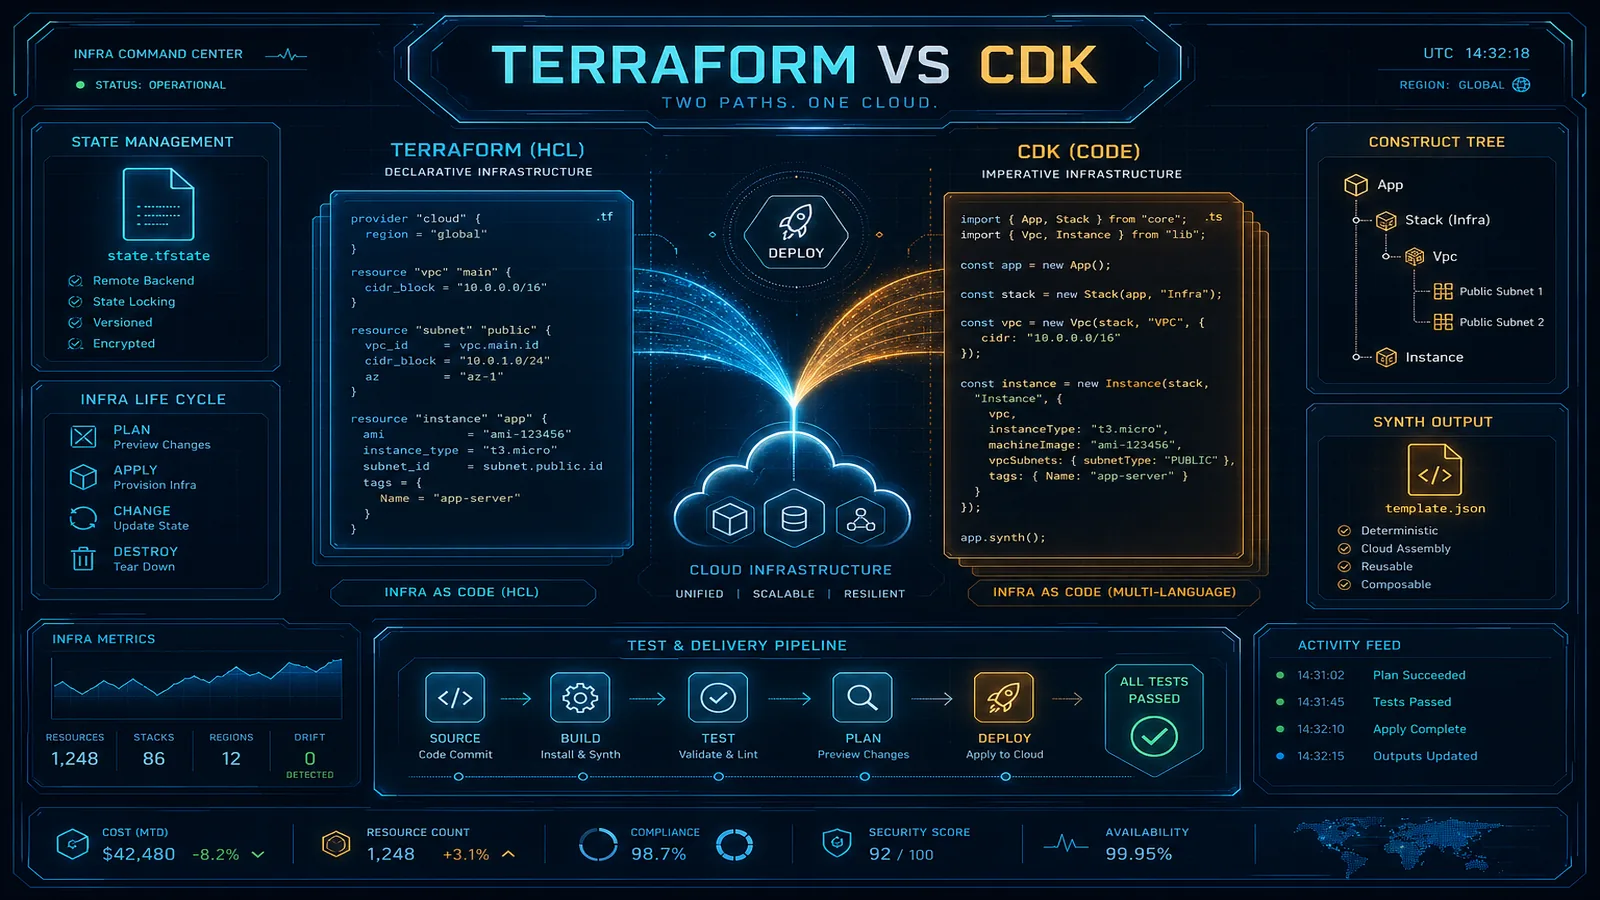
This post is Terraform/OpenTofu vs CloudFormation/StackSets for enterprise AWS. It is not Terraform vs CDK (authoring frameworks), not Terraform vs Pulumi (language choice), and not CloudFormation best practices (how-to for CFN only).
Artifacts: IaC decision matrix, enterprise criteria worksheet CSV.
Benchmark pattern (not a cited client) — 40-account AWS Organization, mixed Terraform app stacks + manual account baselines. Platform team deployed StackSets (Config, GuardDuty, CloudTrail Hooks) to 3 OUs — rollout 9 weeks → 3 weeks. App teams stayed on Terraform/OpenTofu; no app stack migration.
Decision in one table
| Need | Terraform/OpenTofu | CloudFormation/StackSets |
|---|---|---|
| App team daily deploys | Default | Possible via CDK→CFN |
| Org-wide baseline | Secondary | Default |
| Multi-cloud / third-party providers | Default | Poor fit |
| No remote state ops | Weak | Default |
| GovCloud native packaging | Partition config | Stronger |
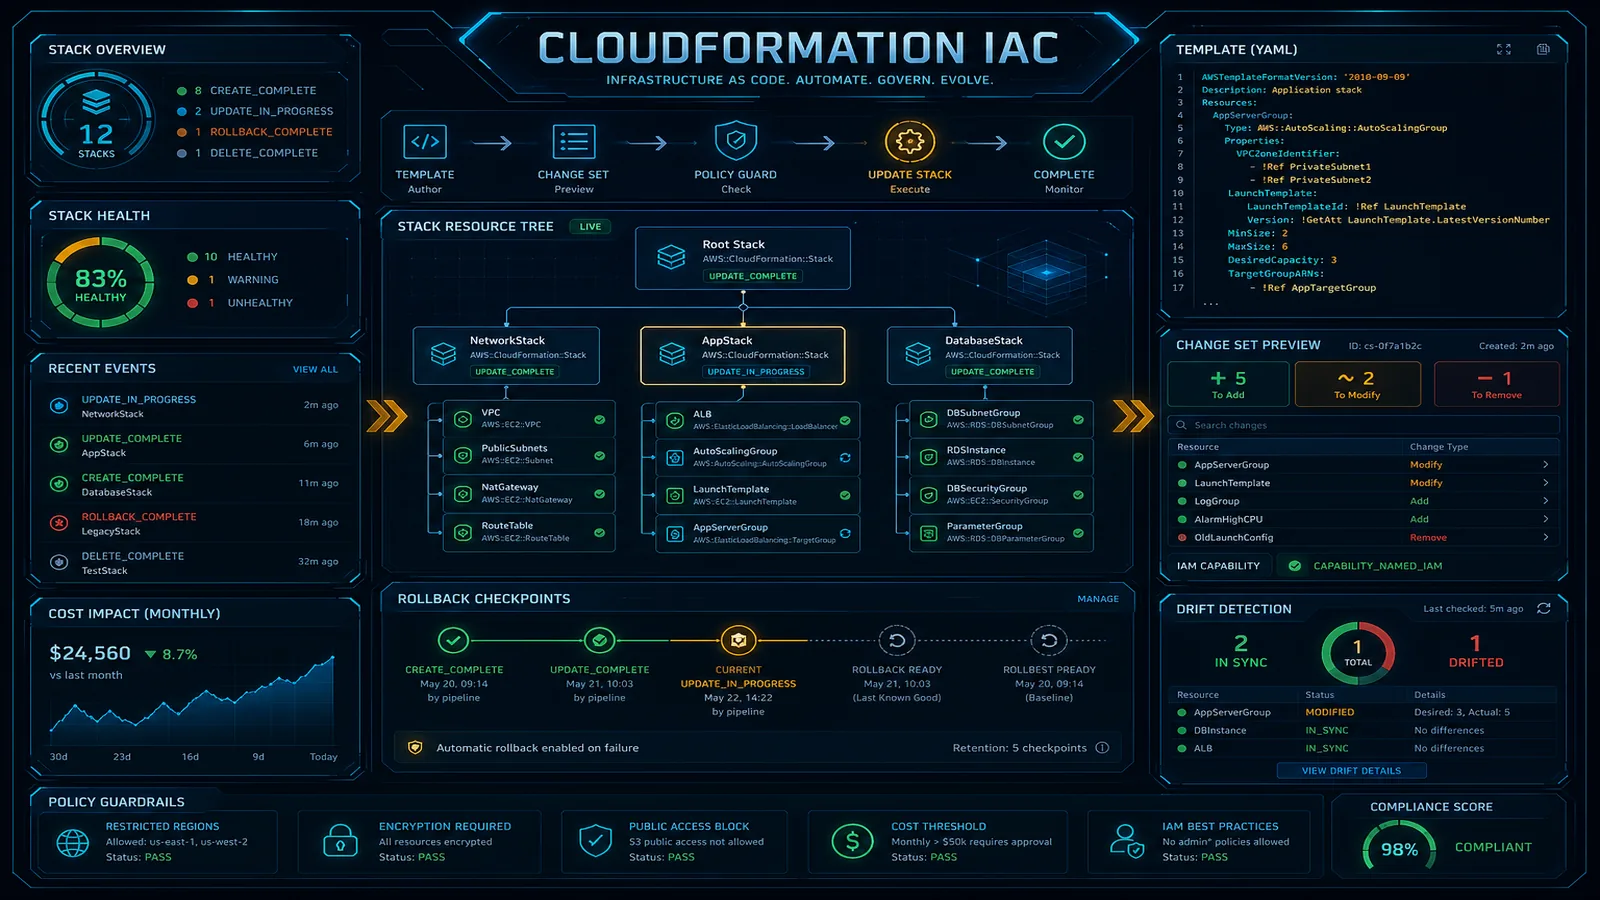
| Drift detection | CI + plan | Built-in stack drift |
Opinionated take: Hybrid — StackSets for platform baseline, Terraform for application stacks. One-tool mandates fail when security needs org rollouts and apps need HCL velocity.
CloudFormation / StackSets — when it wins
- Organizations auto-deployment — new accounts in OU get baseline stacks automatically
- CloudFormation Hooks — proactive compliance (e.g., S3 public access block) at deploy time
- No S3 state bucket — one less secret-leak surface
- Service Catalog integration for governed self-service
# Context: CloudFormation StackSet excerpt — service-managed permissions (July 2026)
# Deploy baseline to entire OU; enable trusted access in Organizations first.
Resources:
  GuardDutyEnable:
    Type: AWS::GuardDuty::Detector
    Properties:
      Enable: true
Platform team owns the template; member accounts receive stack instances without local Terraform.
Terraform / OpenTofu — when it wins
- for_each / dynamic blocks for N environments without copy-paste YAML
- Terraform Registry modules shared across repos
- Multi-provider — AWS + Datadog + Cloudflare in one plan
- Existing estate — migration cost dominates switch-to-CFN math
# Context: Terraform 1.8+, AWS provider ~5.x — app stack pattern
resource "aws_ecs_service" "api" {
  for_each = var.environments
  name     = "api-${each.key}"
  cluster  = aws_ecs_cluster.main.id
  # ...
}
What broke — StackSets rollout
What broke — Week 2 of OU-wide StackSets: 12 of 40 accounts stuck PENDING. Root cause: S3 template bucket policy used
"AWS": "*"initially, then over-corrected to deny member account roles. Fix: service-managed permission role ARN patternarn:aws:iam::*:role/stacksets-exec-*in bucket policy. Lesson: test on 2-account OU before prod OU.
Hybrid reference architecture
Management account
├── StackSets (service-managed) → Config, GuardDuty, CloudTrail, Hooks
├── SCPs (Organizations)
└── Delegated admin for StackSets

Member accounts (app teams)
└── Terraform/OpenTofu → ECS, RDS, Lambda (remote state in shared account)
Align with enterprise governance OU taxonomy.
When NOT to use each
| Tool | Skip when |
|---|---|
| Terraform only | Org needs Hooks + auto-deploy to new accounts |
| CFN only | 500+ existing Terraform resources, multi-provider |
| CDK instead of both | Team wants neither TypeScript nor HCL — rare |
What to do this week
- Score your org on enterprise-criteria-worksheet.csv.
- Run decision matrix — assign platform vs app layer.
- If no StackSets baseline: pilot 2 accounts in one OU before org-wide.
- If Terraform state on S3: verify versioning + MFA delete + lock table today.
- Document hybrid pattern in internal wiki — stop the “Terraform vs CFN” religious war.
Reproduce this — Fill enterprise-criteria-worksheet.csv with weights 1–5 for your constraints. Sum weighted scores. If
org_wide_stacksetsweight ≥ 4 and CFN score wins, start StackSets pilot — do not migrate app Terraform first.
What this post doesn’t cover
- CDK authoring depth — Terraform vs CDK guide.
- Application Composer visual IaC — Application Composer post.
- Full Terraform state migration — state management guide.
- Pulumi — OpenTofu vs Pulumi.
Related: DevOps pipeline setup · Enterprise governance
Frequently asked questions
When should we use CloudFormation instead of Terraform on AWS?
Use CloudFormation (especially StackSets) for org-wide baseline every account must inherit — Config rules, GuardDuty enrollment, CloudTrail, SCP-adjacent Hooks. CFN has no remote state to secure, native drift detection, and first-class Organizations integration. Use Terraform for application teams shipping daily who need HCL loops, multi-provider modules, and existing Terraform estate.
When should we NOT standardize on CloudFormation only?
Skip CFN-only if your teams already operate 500+ Terraform resources, you integrate third-party providers (Datadog, MongoDB Atlas) in the same stack, or developers refuse YAML/JSON without CDK. Forcing migration from Terraform to CFN for app stacks rarely pays back — hybrid (StackSets baseline + Terraform apps) is the enterprise norm.
How does this differ from Terraform vs AWS CDK?
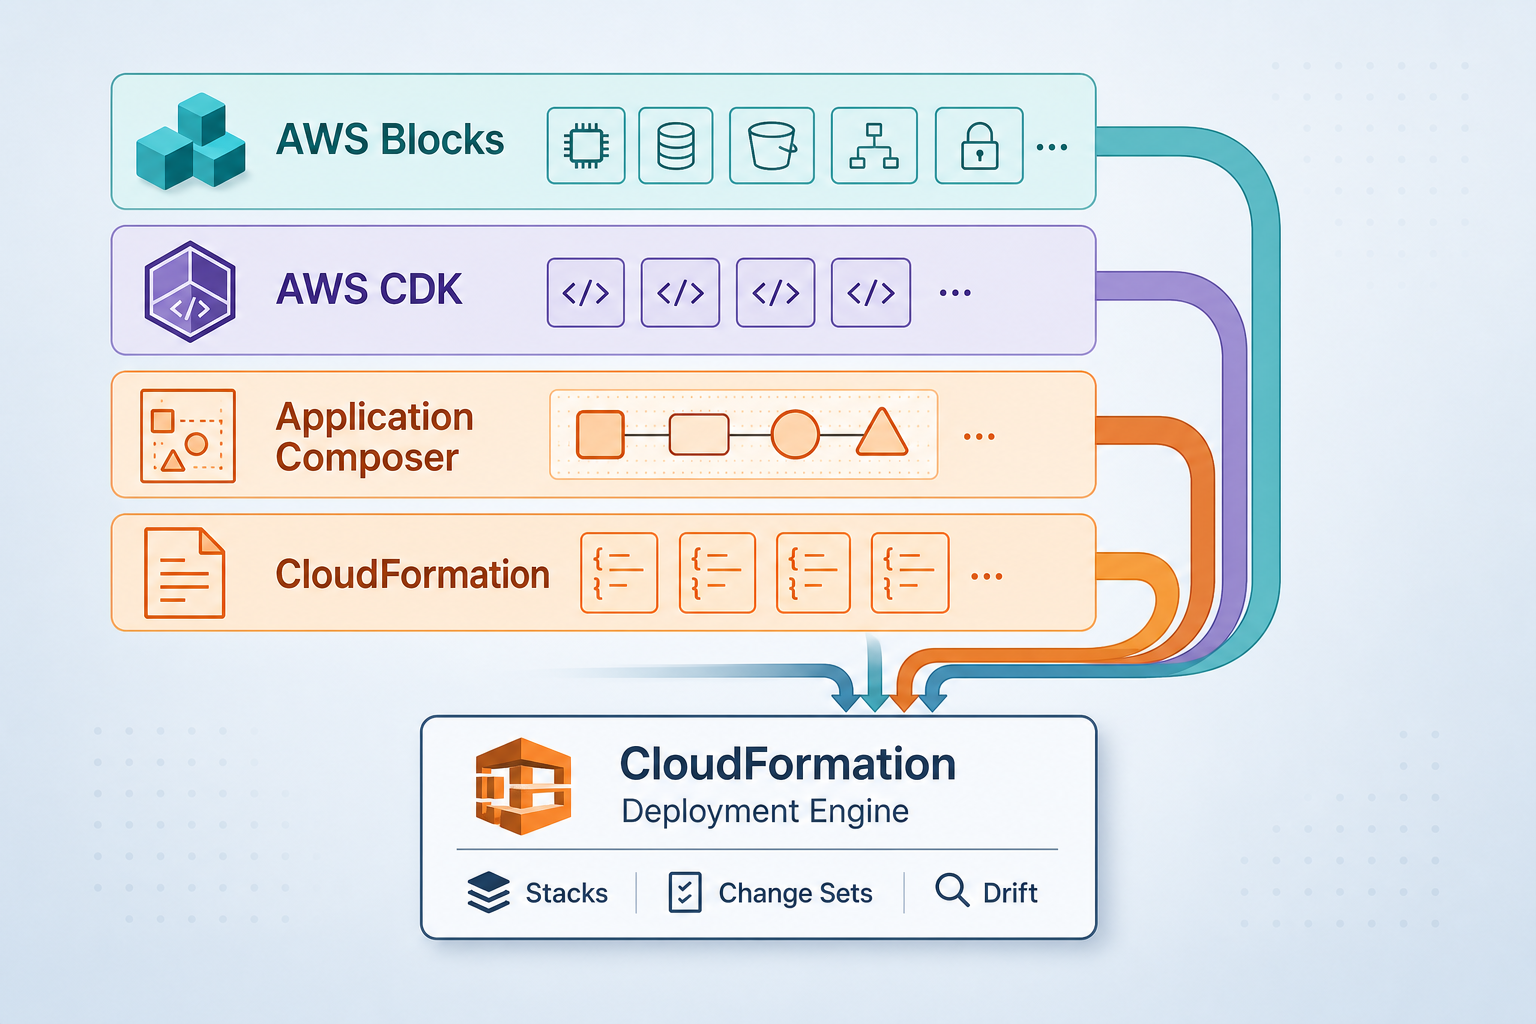
CDK synthesizes to CloudFormation — it is an authoring layer, not a deployment engine alternative to Terraform. This post compares Terraform/OpenTofu (independent state, multi-cloud) vs native CloudFormation/StackSets (AWS-managed, no state file). For CDK vs Terraform authoring, see the CDK decision guide.
What breaks during org-wide StackSets deployment?
Common failures: trusted access to StackSets not enabled in Organizations, S3 template bucket policy too permissive or too restrictive for member accounts, Hooks package not replicated to target regions. Symptom: stack instances stuck in PENDING, partial account enrollment. Fix: validate delegated admin account and service-managed permissions before OU-wide rollout.
Does Terraform work in AWS GovCloud?
Yes, with partition-aware provider configuration (aws-us-gov). CloudFormation has native GovCloud partition packages and FedRAMP-adjacent workflows. Many public-sector teams use CFN for baseline and Terraform for apps — verify provider resource availability per partition before standardizing.
What could go wrong with Terraform remote state?
S3 state bucket without versioning and MFA delete, DynamoDB lock table missing, or state readable by overly broad IAM policies. A leaked state file exposes secrets and resource topology. CFN avoids this by storing state in AWS-managed stacks — trade-off is less flexible workflow.
AWS Cloud Architect & AI Expert
AWS-certified cloud architect and AI expert with deep expertise in cloud migrations, cost optimization, and generative AI on AWS.